1
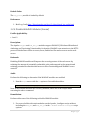
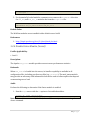
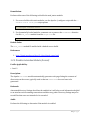
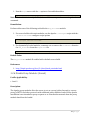
level configuration and every virtual host that is SSL enabled. Also ensure that SSLStaplingCache is set to one of the three cache types similar to the examples below. SSLUseStapling On SSLSessionCache "shmcb:logs/ssl_staple_cache(512000)" - orSSLSessionCache "dbm:logs/ssl_staple_cache.db" - or SSLSessionCache dc:UNIX:logs/ssl_staple_socket Default Value: Default values are: SSLUseStapling Off SSLSessionCache no default value References: 1. http://en.wikipedia.org/wiki/OCSP_stapling -‐ OCSP Stapling 2. http://httpd.apache.org/docs/2.4/mod/mod_ssl.html-‐ Apache SSL Directives 1.7.10 Enable HTTP Strict Transport Security (Scored) Profile Applicability: • Level 2 Description: HTTP Strict Transport Security (HSTS) is an optional web server security policy mechanism specified by an HTTP Server header. The HSTS header allows a server declaration that only HTTPS communication should be used rather than clear text HTTP communication. Rationale: Usage of HTTP Strict Transport Security (HSTS) helps protect HSTS compliant browsers and other agents from HTTP downgrade attacks. Downgrade attacks include a variety of man-‐in-‐the-‐middle attacks which leave the web communication vulnerable to disclosure and modification by forcing the usage of HTTP rather than HTTPS communication. The sslstrip attack tool by Moxie Marlinspike released in 2009 is one such attack, which works when the server allows both HTTP and HTTPS communication. However a man-‐in-‐the-‐ middle HTTP-‐to-‐HTTPS proxy would be effective in cases where the server required 88 | P a g e