1
Security Technical
11
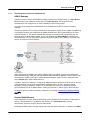
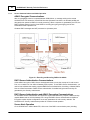
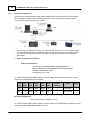
SCM Configuration: Every SCM has various configuration parameters that include an SCM address,
communication parameters, and static session information. SCADAPack E RTU Virtual SCMs can be
configured through command line text entry, through a plug in media module (e.g. Compact Flash card
on SCADAPack ES or SCADAPack ER), or through local USB peripheral communication port using
SCADAPack E Configurator (SCADAPack 300E). The security files for Compact Flash card or
SCADAPack E Configurator loading of the configuration is managed by a Windows® Security
Administrator application.
SCM Address: SCADAPack E RTU’s Virtual SCM address is obtained directly from the device’s
configured DNP3 node address. Every SCM on a shared or networked communications link needs to
have a unique SCM address (and therefore unique DNP3 address). Addresses in the range 1 – 65519
are valid addresses for both DNP3 and SCM. Address 0 is not a valid SCADAPack E SCM address and
can not be used as an SCADAPack E RTU DNP3 node address when using AGA12 security.
Security Administrator: The SCADAPack E application used by the person responsible for security
administration in a network. This application is a type of security Authority 9 that retains and provides
security configuration files for the rest of the system. It should be operated by corporate level security
administration personnel.
Session: A session is a bidirectional virtual communications channel established between a specific
pair of devices. In the case of AGA12 on SCADAPack E RTUs, a session is established between each
pair of SCADAPack E virtual SCM’s. A session has a type indicating it as static or dynamic. Static
sessions have cryptographic and other parameters that are configured in SCM configuration data.
Dynamic sessions have negotiated cryptographic parameters and vary with time and each message sent
on the session. Management of sessions is one of the tasks carried out by the SCADAPack E RTU’s
Virtual SCM. DNP3 similarly establishes a session for communication between two devices. Part of the
DNP3 session's information includes DNP3 Secure Authentication information.
SSPP: SCADA Security Protection Protocol – Defined by the AGA12-2 standard. This is the technical
name of the AGA12-2 protocol that transports session information and secured data between SCMs.
Unique Key: The SCADAPack E security mode requiring that SCADAPack E Configurator nodes be
individually secured (optional).
Update Key: DNP3 Secure Authentication terminology for the secret key
communicate with each other.
10
known to devices that